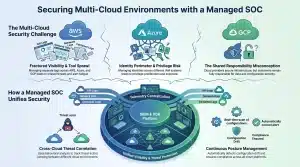
Modern cyber threats bypass traditional antivirus and firewalls by exploiting expanding attack surfaces, cloud environments, and remote workforces. SOC services (Security Operations Center services) deliver 24/7/365 continuous threat monitoring, real-time alert triage, and rapid incident response preventing costly data breaches and simplifying compliance without requiring an expensive, in-house security team.
Our scalable, managed SOC solutions, customized to give mid-market enterprises robust, round-the-clock cyber resilience.
What Are SOC Services?
SOC services provide security experts who can use threat intelligence and SIEM/XDR systems to continuously monitor, identify, analyze, and eliminate cyber threats from your entire digital environment, including endpoints, cloud, servers, and networks before they lead to any disruption or financial damage to your organization.
Why Businesses Need SOC Services
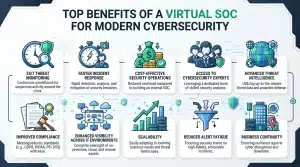
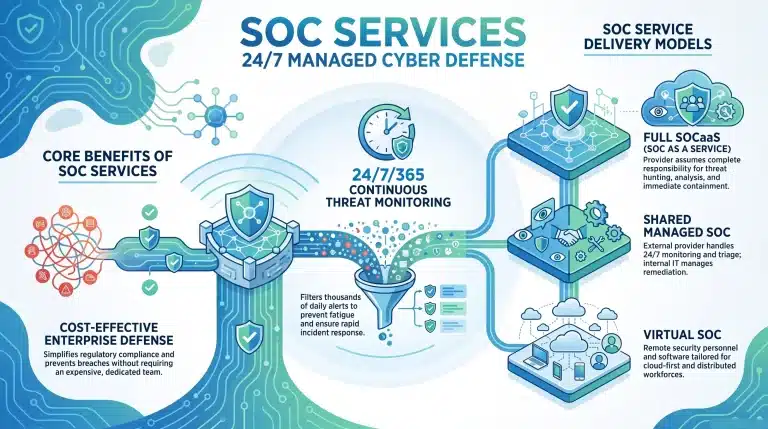
As threats continue to grow increasingly complex, the importance of having constant security monitoring cannot be overstated. The Security Operations Center (SOC) can help businesses detect any suspicious activities and respond to them at all times of the day. The SOC can filter thousands of alerts per day and validate any potential threats, which means that there will be no alert fatigue and much faster incident response. The SOC can help businesses comply with regulations by providing continuous monitoring, auditing and log management, and even save on hiring a dedicated security team.
SOC Service Delivery Models
All business organizations have their own budgets, current IT architecture, and compliance issues. Four main SOC services can be offered to organizations:
- Full SOCaaS: The provider assumes full responsibility for your SOC operations. It is responsible for all tasks ranging from 24/7 continuous logging and threat hunting to instant incident analysis and immediate containment. Recommended to organizations lacking internal SOC teams.
- Shared Managed SOC: The roles are shared by the employees of your organization and SOC provider. While the external SOC is responsible for 24/7 monitoring, logging, and triage of alerts, the internal IT team is responsible for remediation and configuration settings management. Best fit for experienced IT professionals needing 24/7 availability and escalation to experts.
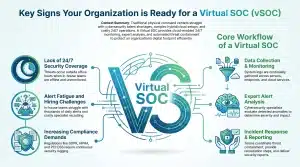
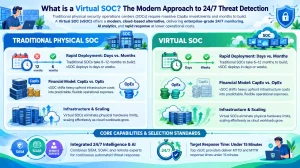
- Virtual SOC: Flexible surveillance system offered using software and security personnel working remotely. Perfect for businesses designed in the cloud, remote companies, and companies with employees spread around the globe.
Key Selection Criteria for a SOC Provide
It is important to choose the appropriate SOC partner to ensure your cybersecurity preparedness is up to the mark. A good SOC partner needs to be someone who brings together qualified security experts and powerful monitoring systems to effectively identify, investigate, and respond to security threats. The SOC needs to work harmoniously with current security products and infrastructure, as well as offer SLAs, quick incident resolution, transparency, and compliance.
Common Selection Mistakes to Avoid
- Price-Based Selection Only: SOC service providers that offer discounts have used only automated scripts and basically work as expensive notification forwarding systems.
- Ignoring Analyst Experience: Even sophisticated software can’t do much if it’s not backed up by competent analysts with experience under their belt. Make sure your service provider utilizes certified, experienced security analysts.
- Escalation Procedures: Lack of escalation procedures can cause unnecessary delays in reacting to zero day and ransomware attacks.
Secure Your Organization with IBN Technologies
IBN Technologies offers a full-fledged, intelligence-enabled SOC service that is specifically crafted to ensure the closing of any security holes and improving the organization’s preparedness. By offering around-the-clock monitoring, thorough threat investigation, and proactive incident handling, companies will be able to have continuous insight into the status of their security landscape while freeing up the load from their IT staff. Learn more about how our IBN Technologies Managed SOC Services provide enterprise-level protection 24 hours a day.
Consult our cybersecurity professionals now.
Need Managed SOC and SIEM Services for your 2026 project?
Get a free consultation with our tech team — no commitment.
Frequently Asked Questions
Not at all. High-quality SOC services are completely agnostic to vendors and are developed in such a way that they work together with your existing security setup including firewalls, EDR agents, identity management apps, cloud environment (AWS, Azure, Google Cloud).
The continuous log management, real-time monitoring, auditing process, and incident response procedures are all provided by managed SOC services to fulfill the following regulatory requirements: ISO 27001, HIPAA, PCI-DSS, SOC 2, GDPR, and CMMC.
Absolutely. Contemporary cyber adversaries often go after mid-market companies because they know they do not have enterprise-level protections in place. SOCaaS services offer enterprise-level cybersecurity solutions that scale with the budget and capabilities of emerging companies without spending tons of money upfront.