Organizations and government bodies in Kolkata and Eastern India are confronted with increasing cyber threats due to their movement from legacy systems to the cloud, supply chain relationships, and infrastructural threats. The need for adopting VAPT testing services as an approach to avoid severe punishment according to the requirements of the DPDP Act and CERT-In becomes imperative as they are required to rectify certain critical flaws, which automated scanning is unable to detect.
Why VAPT Matters for Kolkata Organisations
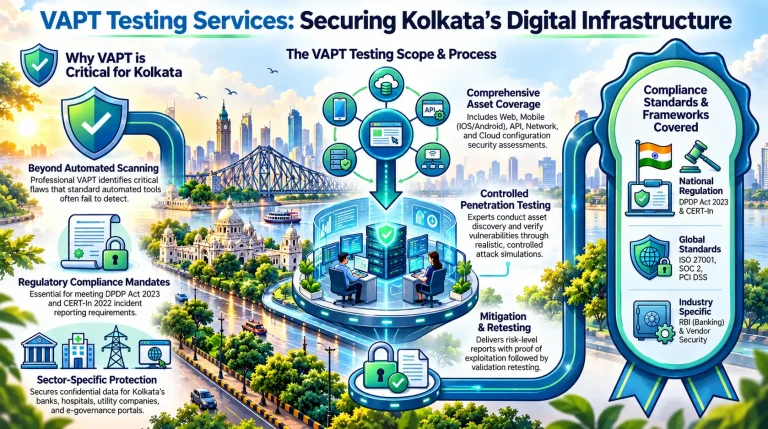
Organizations operating in different sectors including banks, hospitals, manufacturing units, information technology, educational institutions and government bodies in Kolkata depend on their digital systems and confidential information. Vulnerabilities in their web applications, cloud systems, API and networks can leave them vulnerable to attacks, breaches, malware infections and even disruption in services. VAPT allows organizations to recognize vulnerabilities and strengthen their security measures.
What VAPT Testing Services Include
An end-to-end VAPT analysis focuses on analysing the key digital assets of an organization as per its technological environment and the level of risks and compliance standards. The coverage usually entails:
Web Application VAPT
Detection of vulnerabilities related to authentication, access control, input validation, session management, encryption, and business logic, among others like SQL injection, XSS, and sensitive data leakage.
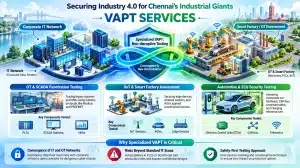
Network Penetration Testing
Evaluation of the security of internal and external network, servers, firewalls, VPNS, AD (Active Directory), and wireless environments.
API Security Testing
Assesses security of API Authentication, Authorization, Token security, Input Validation, Data Exposure, Rate limiting, and Business Logic issues in connected applications.
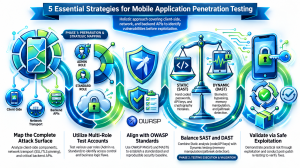
Mobile Application VAPT
Checks Android and iOS applications for Insecure Storage, Weak Encryption, Insecure Authentication, Insecure API Communication, and Reverse Engineering Risks.
Cloud Security VAPT
Performs review of cloud configuration, identities, permissions, storage, VMs, Containers, Networking and Encryption issues.
Red Team Testing
Conducts realistic cyber-attack simulation to test an organization’s preparedness in prevention, detection, and mitigation of advanced attacks. Ideal for mature organizations and service providers.
VAPT for Kolkata’s Public Sector
The government departments, public sector entities, educational institutions, hospitals, utility companies, and the e-governance portal deal with a lot of confidential information and important services. The process of VAPT assists in detecting any vulnerabilities in the portals of citizens, payment gateways, databases, and internal networks without causing any major disturbances.
Compliance and VAPT
VAPT does not ensure compliance; it serves as important evidence for review, auditing, assessment by clients, and risk management processes.
According to CERT-In’s Directions 2022, covered entities need to report the listed cyber incidents within six hours from the time of detection or reporting. Another legislation Digital Personal Data Protection Act, 2023 states that data fiduciaries must take reasonable measures to protect personal data.
The scope of VAPT testing services may cover ISO 27001, SOC 2, PCI DSS, RBI, CERT-In, data protection, and vendor security needs. Nevertheless, testing is not aimed at audit; an organisation must fix any vulnerabilities found and perform retesting.
How the VAPT Process Works
The VAPT process starts with the definition of the scope, goals and systems which will be involved in the testing process. Security experts conduct an asset discovery and vulnerability assessment to detect any possible weak links in applications, networks, APIs and clouds. This data is verified through controlled penetration testing to assess its actual impact. The result is provided in the form of a report containing risk levels, proof of exploitation and mitigation measures, along with retesting the system.
Choosing a VAPT Company in Kolkata
While choosing a VAPT provider, the organisation should take into consideration aspects beyond pricing and analyse the experience of the provider in assessing various components including web application, APIs, mobile app, cloud environment, and networks. Experienced security professionals have the capability of discovering real-life vulnerabilities that automated scanning tools cannot discover. Other important aspects are industry experience, complete reporting, handling of sensitive data, retesting capabilities, and CERT-In empanelment.
IBN Technologies offers best VAPT testing services which comprises web security testing, mobile security testing, API testing, network security testing, and cloud security testing. With expertise in professionals and comprehensive reporting in its kitty, IBN Technologies equips any organization to defend against all sorts of cyber-attacks.
Contact us today for a comprehensive security assessment and proactive cyber risk protection.
Need VAPT Services for your 2026 project?
Get a free consultation with our tech team — no commitment.
Frequently Asked Questions
Vulnerability Assessment and Penetration Testing (VAPT) evaluates security weaknesses across network infrastructure, applications, and cloud environments. It helps organizations identify and address vulnerabilities that could expose confidential information or increase the risk of cyberattacks, while supporting applicable security and compliance requirements.
Automated vulnerability scanning primarily identifies known or detectable security weaknesses. VAPT testing services combine automated scanning with manual penetration testing performed by security experts to validate vulnerabilities and identify deeper security and business-logic weaknesses.
VAPT can support security and compliance requirements associated with standards and regulatory frameworks such as ISO 27001, SOC 2, PCI DSS, RBI requirements, the DPDP Act 2023, and applicable CERT-In directions. Specific VAPT requirements depend on the applicable framework, organization, and scope.
A comprehensive VAPT assessment can cover web applications, Android and iOS mobile applications, internal and external networks, APIs, cloud platforms, and other in-scope infrastructure. Red team exercises may also be conducted as a separate or extended assessment to evaluate security defenses against realistic attack scenarios.