Modern organizations need to work in an environment that requires stringent security and data protection measures. For any company dealing with Software as a Service, cloud technologies, or any form of technology for that matter, security measures will play a very critical role in ensuring that customers, partners, and stakeholders trust you with their data. Security is no longer just the realm of the IT department. It has now become a key business enabler of trust and credibility.
The business value of SOC 2 compliance extends well beyond satisfying compliance requirements. Through independent verification of the security processes of an organization, SOC 2 helps build trust of customers, simplify vendor assessments, cut down sales friction, and improve competitive advantage. For fast-growing companies, SOC 2 is not just another audit. It is a valuable investment into growth potential.
What is the business value of SOC 2 Compliance?
SOC 2 ensures an organization has sufficient controls over its customer information and proper operation of its services. This is mainly in terms of security, availability, confidentiality, privacy, and processing integrity.
Businesses stand to benefit from this in four main ways:
- Gaining bigger customers.
- Reducing sales time.
- Creating customer trust.
- Better operations internally.
The exact benefits will depend on market, customer needs, scope of SOC 2, and current security maturity level. However, when it comes to businesses offering their products to enterprise customers, the cost of not having SOC 2 can be very high.
The 5 Pillars of Business Value in SOC 2
- Access Enterprise Revenue and Reduce Sales Cycles
The most obvious ROI of SOC 2 certification is achieved through the sales process.
- Remove Sales Obstacles: Prospective mid-size and Fortune 500 companies require security clearance before signing any agreements. Without a SOC 2 certification, such agreements are stalled forever in vendor security reviews.
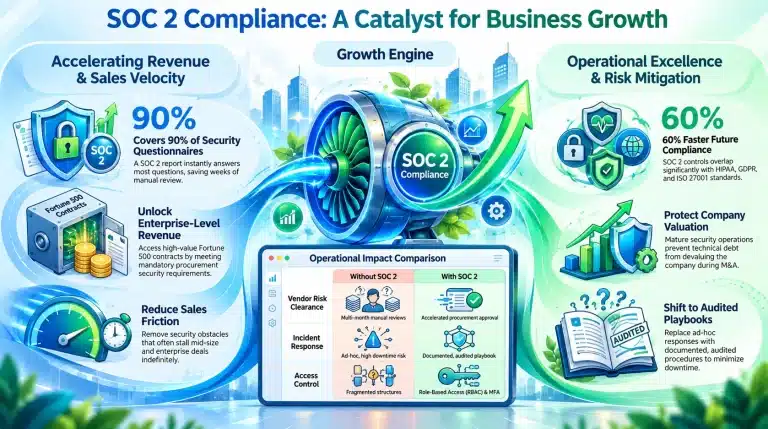
- Skip Time-Consuming Questionnaires: Procurement security questionnaires typically consist of 200 or more questions on security. Providing a SOC 2 Type 2 report covers 90% of such questions right away, saving many weeks of review.
- Sell Up-Market: SOC 2 certification provides access to high-revenue opportunities in enterprises that can use their procurement policy not to deal with uncertified vendors.
- Differentiating in a Crowded Market
In markets where software solutions are highly competitive, the functionalities can be replicated overnight, but the trust cannot.
Showing SOC 2 certification helps prove that your company is following high standards of security measures. By being in competition with companies or platforms which have not gone through third-party audits, your SOC 2 report acts as a great branding tool.
- Preventing Financial & Reputational Ruin
Security incidents can disrupt operations, damage customer trust, increase remediation costs, and lead to lost business opportunities. SOC 2 compliance helps organizations reduce these risks by strengthening security controls and improving their ability to prevent and respond to threats.
| Security Incident Impact | Without SOC 2 Controls | With SOC 2 Controls |
| Vendor Risk Clearance | Multi-month manual reviews | Accelerated procurement approval |
| Incident Response | Ad-hoc, high downtime risk | Documented, audited playbook |
| Access Control | Fragmented permission structures | Role-Based Access Control (RBAC) & MFA |
| Brand Impact | Reputational damage & customer churn | Proven commitment to data integrity |
By implementing SOC 2 controls, companies build operational resilience that minimizes the likelihood and severity of security breaches.
- Operational Efficiency & Scalable Governance
SOC 2 Compliance necessitates that organizations move away from ad hoc approaches to structured and consistent infrastructure operations.
- Internal Policies: Access controls, change management, and disaster recovery procedures prevent any possibility of creating a single point of failure.
- Employee Duties: Security training for employees and well-defined guidelines concerning employee recruitment/de-recruitment prevent any threat to internal infrastructures.
- Multi-Framework Compliance Easy: Security controls required for SOC 2 compliance are almost the same as most international standards including ISO 27001, HIPAA, and GDPR. Implementation of SOC 2 compliance helps save up to 60% of time in future compliance.
- Investor Confidence & Valuation Multiples
Technical debt and security infrastructure assessment is done when raising capital, doing M&A, etc. Technical debt that involves security may reduce the valuation of a company by a lot or delay the transaction. If you have a Type 2 SOC 2 report, then you know for sure that there is maturity in your operations.
Strategic Implementation: How to Maximize ROI
If SOC 2 is to create meaningful business value instead of being viewed as just another compliance burden:
- Scope Realistically: Audit all five Trust Services Criteria at once only when there is legal necessity. Audit only Security (which is mandatory) along with either Confidentiality or Availability based on your main platform offering.
- Leverage Compliance Automation: Today’s compliance management systems can collect continuous evidence automatically, saving 70% of manual preparation internally.
- Enable the Sales Team: Train account managers to actively provide the SOC 2 executive summary in the later stages of contract negotiations.
- Treat Compliance as Continuous: Combine continuous monitoring with engineering processes to avoid the annual audit panic.
Conclusion
SOC 2 compliance is not just another cost or a burden but an actual investment in revenue velocity and market position for organizations. Through proving that your customer information is safeguarded via independent controls, your organization eliminates procurement costs, improves brand integrity, and turns security into a reliable growth engine.
If you are an expanding business venturing into security-sensitive markets, working with an experienced compliance and managed security services provider like IBN Technologies can make all the difference. Through providing you with comprehensive gap analysis and control monitoring services, the right managed security service provider will ensure the sustainability of your compliance infrastructure, giving your organization enough room to innovate and grow.
Need SOC 2 Services for your 2026 project?
Get a free consultation with our tech team — no commitment.