VAPT testing services in Hyderabad assist organizations in identifying and resolving vulnerabilities in their web applications, APIs, cloud environments, networks, and many more business-critical systems to prevent malicious exploitation of these vulnerabilities by any attacker. With an ever-increasing number of cyber-attacks, data breaches, ransomware attacks, and compliance requirements, the VAPT process will enable organizations to improve their security measures.
Why Companies in Hyderabad Need VAPT?
Hyderabad is an important center for technology with its HITEC City, Gachibowli, Financial District, and Genome Valley. The city is home to leading technology companies, innovative SaaS companies, research institutions such as IIIT Hyderabad, and multinational pharmaceutical giants; consequently, it hosts a large amount of consumer data, financial information, intellectual property, and cloud computing services.
Digital threats in the urban area are in line with dual economy engines of the urban area:
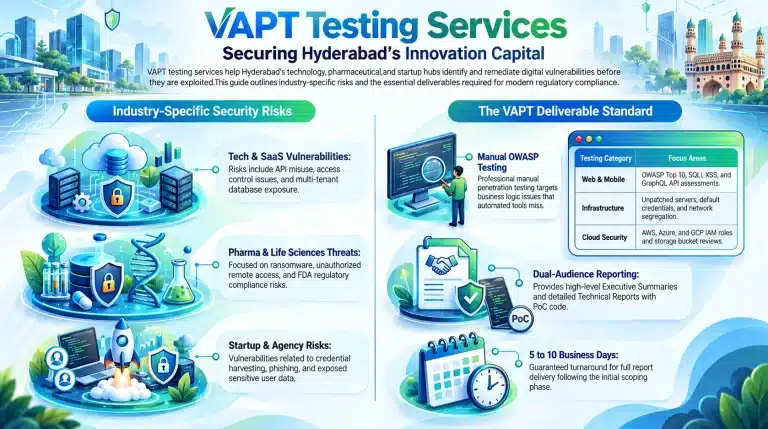
- Technologies and SaaS companies: Risks related to API misuse, access control issues, and multi-tenant databases causing exposure for international corporate deals.
- Pharmaceuticals and life sciences: Ransomware attacks, unauthorized remote access to production systems, and compliance risks based on US FDA and Indian regulatory guidelines.
- Service agencies and startups: Risk related to credential harvesting, phishing attacks, and open portals posing risk to sensitive user data.
Vulnerability and pen testing help identify and remediate such digital threats based on a legal and signed scope rather than having them discovered via a data breach.
What We Test for Hyderabad Companies
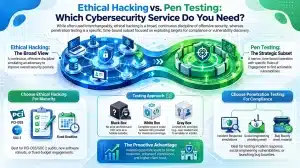
Web Application VAPT: Full assessment of OWASP Top 10 including SQL injection, Cross Site Scripting (XSS), broken access control, and authentication vulnerabilities in client portals and web application systems.
API & Mobile VAPT: End-to-end VAPT test of REST and GraphQL APIs as well as native mobile applications on Android and iOS operating systems, as per OWASP Mobile & API Top 10.
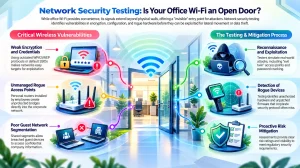
Network & Infrastructure Security: Vulnerability assessment of internal and external networks for vulnerabilities related to exposed/default credentials, vulnerable/unpatched servers and network services segregation.
Cloud Configuration Review: Assessment of cloud infrastructure (AWS, Azure, GCP) for any exposed storage buckets and overly permissive IAM roles.
Regulatory Compliance Mandates
The regulatory landscape and security requirements continue to change, and this means that organizations are now required to show that they have appropriate security measures implemented in their environments. It is at this point that VAPT testing services in Hyderabad plays a key role since it allows for the identification of vulnerabilities that could potentially be exploited, and due diligence on the part of the organization is shown.
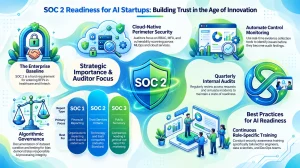
DPDP Act 2023 brings to focus the necessity of implementing proper protection measures for personal data, on the other hand, CERT-In requires that proactive monitoring is done. Moreover, internationally renowned standards like ISO 27001, SOC 2, and PCI DSS v4.0 mandate periodic security assessments to verify the efficacy of the security controls put in place. Due to this reason, organizations today undertake VAPT exercises not just for regulatory compliance but also for vendor assessment and onboarding of customers.
What It Costs, and the SLA You Should Expect
VAPT pricing is determined after a free scoping call, ensuring you pay only for your active attack surface a single web application cost significantly less than a full multi-cloud platform.
What You Receive in Writing:
- Fixed Commercial Proposal: Clear scope pricing with absolutely no hidden costs through hourly surprises.
- Manual OWASP Testing: Manually conducted penetration test focusing on business logic issues which automated tools can never find.
- Dual-Audience Reporting: Executive Summary report for executives along with the Technical Report, which consists of CVSS scores, risks, and Proof of Concept (PoC) code for developers.
- Guaranteed Turnaround: Delivery of the full report within 5 to 10 business days from scoping.
- Vulnerability Verification: Free re-test and then a VAPT Security Attestation Certificate.
Choosing the Right VAPT testing services Provider in Hyderabad
Choosing an organization for VAPT testing services in Hyderabad means choosing a company that not only conducts automatic scans, but also manual penetration testing based on the OWASP standards, gives remediation report, is compliant, and provides retesting.
IBN Technologies can help your Hyderabad-based company to find out and fix any vulnerabilities in the web applications, APIs, networks, cloud computing environment, and enterprise applications that might exist in your organization’s IT infrastructure.
Would you like to schedule a free VAPT scoping consultation?
Need VAPT Services for your 2026 project?
Get a free consultation with our tech team — no commitment.
Frequently Asked Questions
A VAPT assessment can cover web applications aligned with the OWASP Top 10, native Android and iOS applications, REST and GraphQL APIs, cloud configurations across AWS, Azure, and GCP, external and internal perimeter networks, and IT infrastructure, depending on the defined scope.
VAPT can provide evidence of vulnerability identification and remediation processes that support an organization's security safeguards under India's regulatory and compliance landscape. It can also help organizations proactively identify and address vulnerabilities in line with applicable CERT-In directions and security frameworks such as ISO 27001, SOC 2, and PCI DSS v4.0.
A typical VAPT engagement may take approximately 5–10 business days after scoping, depending on the size and complexity of the environment. Deliverables can include an executive summary, a detailed technical report with CVSS scores and proof-of-concept details for developers, a complimentary retest, and a VAPT Security Attestation Certificate.
The cost of VAPT testing services is typically determined during the scoping process and depends on the size of the active attack surface, such as IP addresses, web portals, APIs, or mobile applications included in the assessment. A defined scope helps establish the testing requirements and overall engagement cost.