AI startups move fast. The models come out weekly, the data pipelines develop daily, and the corporate buyer demands security maturity from Day One. The regulators, investors, and procurement departments are all asking the same question: Can you be trusted with sensitive data? SOC 2 is the framework that answers “yes” with evidence, not marketing.
Let’s see- what SOC 2 means for AI startups, what auditors and regulators focus on, and how to build a compliance program that doesn’t slow down innovation.
What Is SOC 2 Compliance for AI Startups?
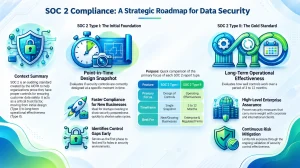
SOC 2 stands for Controls which have been established by the American Institute of Certified Public Accountants (AICPA) with the objective of testing your customer data management process based on five Trust Services Criteria (TSC).
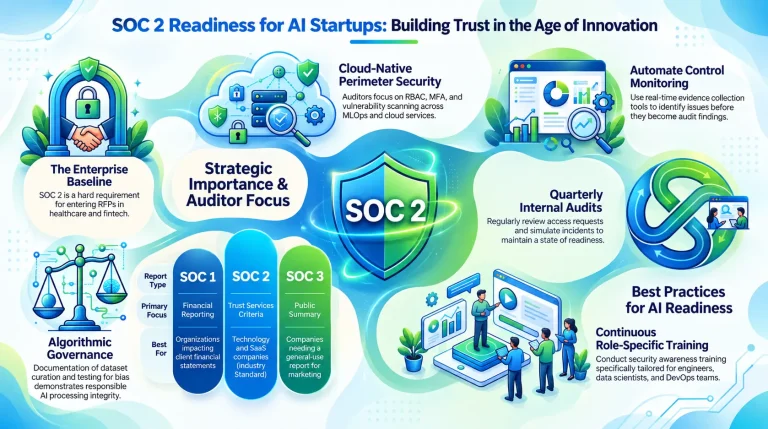
As compared to SOC 1 (financial reporting) and SOC 3 (public summary), SOC 2 is the industry standard for technology and SaaS companies. It involves documented control processes that must run consistently and be audited independently by a certified public accountant.
For AI startups, SOC 2 aligns with how you operate: cloud-native infrastructure, heavy API usage, large training datasets, and complex access patterns across engineering, data science, and MLOps.
Why SOC 2 Is Crucial for AI Startups
Customer Trust and Competitive Edge
Enterprise buyers now treat SOC 2 as a baseline for vendor due diligence. A SOC 2 report shortens procurement cycles, reduces security questionnaires, and signals that you take data protection seriously.
For AI vendors selling into healthcare, fintech, or regulated verticals, SOC 2 often becomes a hard requirement to even enter an RFP or security review.
Managing Sensitive Training Data and Models
AI workloads touch PII, financial records, health data, and proprietary models. SOC 2 forces you to implement:
- Data classification and minimization
- Encryption at rest and in transit
- Access controls and audit trails
- Vendor risk management for cloud and third-party tools
This protects both customer data and your own IP (models, weights, pipelines) from leakage or misuse.
What SOC 2 Regulators and Auditors Focus on for AI Startups
SOC 2 isn’t a generic checklist. Auditors look at how you manage risk in the context of your AI-specific workflows.
Data Privacy and Confidentiality
Regulators expect clear, enforceable practices around personal data used in training and inference:
- Lawful collection and documented consent
- Purpose limitation and data minimization
- Retention and deletion schedules
- Encryption, key management, and secure storage
If your models ingest user behavior, geolocation, or biometric data, you must show how privacy is enforced end-to-end.
Algorithmic Transparency and Bias Management
While SOC 2 doesn’t mandate “fairness” in a legal sense, auditors increasingly probe processing integrity and privacy in AI contexts:
- How datasets are labeled and curated
- Which features drive model decisions
- Whether you test for disparate impact in high-risk use cases (hiring, lending, healthcare)
Documenting model governance, versioning, and validation helps demonstrate responsible AI under SOC 2.
Security Controls for Cloud-Native AI Infrastructures
Most AI startups run on AWS, GCP, or Azure with heavy reliance on managed services (S3, BigQuery, SageMaker, Vertex AI, etc.). Auditors focus on:
- Role-Based Access Control (RBAC) and least privilege
- Multi-factor authentication (MFA) for privileged accounts
- Vulnerability scanning and patch management
- Activity logging, monitoring, and incident response
- Third-party risk management for cloud and tools providers
Your team must show that your security perimeter encompasses all services that interact with your customer’s data or models.
SOC 2 Best Practices for AI Startups
Automate Where Possible
Automated compliance and security will aid in reducing the burden of manual efforts:
- Continual control monitoring (access assessments, configuration scans)
- Evidence collection in real time from cloud/SaaS applications
- Dashboards that give you visibility for audit preparedness
Products such as SecureSlate, Drata, Vanta, or Secureframe can be added to your tech stack and will warn you before minor problems turn into audit findings.
Run Quarterly Internal Audits
Don’t wait for renewal. Every quarter:
- Review access requests, change tickets, and incidents reports
- Test key controls (for instance, MFA enforcement, backup restoration)
- Conduct a simulated incident to test your response process
This will create an accountable environment that keeps you prepared for any audit at any time.
Train Your Team Continuously
Even your most robust technical controls won’t work if employees are working around them. Conduct:
- Security awareness training during hiring and annually
- Training specific to each role for engineers, data scientists, and DevOps teams
- Phishing testing and policy training at least twice a year
Make compliance everyone’s job, not just an IT job.
How to Choose the Right SOC 2 Auditor or Compliance Partner
It is important to identify the correct CPA firm for AI startups because not all firms understand what it entails to work with AI technologies and SaaS platforms. A good partner will be one that has experience with AI businesses, up-to-date methods of auditing, and openness on scope, schedule, and price. It is not enough to just conduct an analysis of controls; there is also need for advice on issues such as data governance, MLOps, and compliance preparedness.
IBN Technologies assists AI and SaaS companies by providing complete audit preparedness and compliance services that make the certification process easy. Through leveraging technology and industry experience, IBN Technologies helps organizations with controls improvement, audit simplification, and compliance goals achievement.
Need VAPT Services for your 2026 project?
Get a free consultation with our tech team — no commitment.
Frequently Asked Questions
SOC 2 provides a foundation for enterprise security due diligence, helping AI companies demonstrate that relevant controls are designed and operating effectively. It can support customer confidence and streamline security reviews. It can also address controls related to sensitive training data, personal information, financial information, and proprietary intellectual property.
Auditors assess controls and risks within the processes and systems included in the SOC 2 scope. For AI startups, relevant areas may include data privacy and confidentiality, such as consent, data minimization, and encryption; algorithmic governance processes; and cloud infrastructure security, including role-based access control (RBAC), multi-factor authentication (MFA), patch management, and vendor risk management.
SOC 2 does not establish a general requirement that AI models must be fair or free from algorithmic bias. However, depending on the system and scope, controls related to processing integrity and privacy may involve documentation of datasets, model-related processes, and risk management. Additional governance and testing may be appropriate for high-impact applications such as lending or hiring.