Modern enterprise architecture is deeply interconnected. Organizations rely on third-party SaaS platforms, cloud service providers, IT contractors, and supply chain management software to maintain daily operations.
While these vendor partnerships drive operational efficiency, they also open significant security vectors. However, most enterprise data breaches originate from a third-party vendor or supply chain partner.
Relying on annual security questionnaires is no longer enough to protect your enterprise. To truly safeguard your attack surface, you must ask a direct question: Can your vendors pass a comprehensive VAPT and Penetration Testing (VAPT) audit?
The Hidden Vulnerability in Your Supply Chain
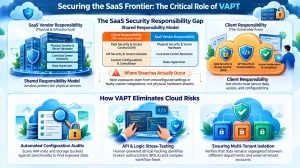
The moment you open your internal network or databases to an outside vendor; their security stance becomes your security perimeter.
One unpatched vulnerability or poor API configuration on the part of the vendor could provide malicious parties the ability to move into your systems while circumventing all of your internal security measures.
Common Third-Party Security Blind Spots:
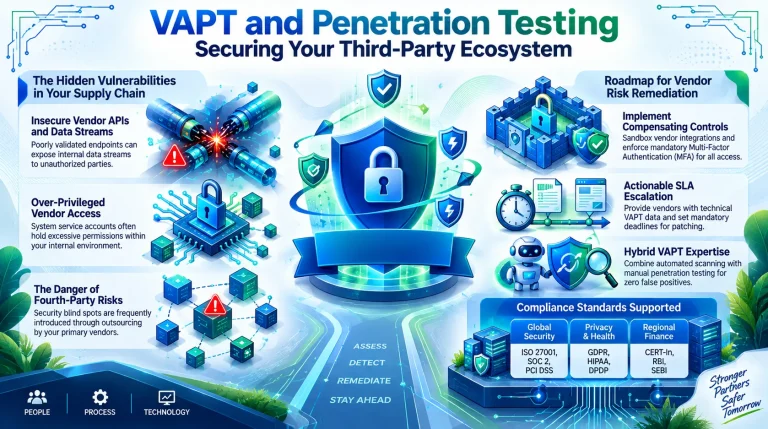
- Insecure Vendor APIs: Unauthorized or poorly validated endpoints exposing your data streams.
- Over-Privileged Access: Vendor personnel and/or system service accounts with overly large permissions within your environment.
- Unpatched Software & Shadow IT: Third-party teams relying on unsecured or outdated software, legacy open-source frameworks or libraries, or unvetted cloud solutions.
- Fourth-Party Risks: Security blind spots introduced through outsourcing by your primary vendor
What to Do When a Critical Vendor Fails a VAPT and Penetration Testing Audit
It is not always easy to find significant vulnerabilities in the software of a vendor, especially if the processes are dependent on the availability of that software. In case a vendor does not pass your assessment, you should take this roadmap for response action:
- Implement Compensating Controls: Reduce vendor network access permissions, place their integrations in a sandbox/DMZ and make Multi-Factor Authentication (MFA) compulsory for all vendors’ access points.
- Issue an Actionable SLA Escalation: Offer the vendor technical data from the VAPT assessment and provide a mandatory deadline for a patch or re-assessment.
- Prepare a Contingency Exit Plan: In case of a critical vendor not addressing significant vulnerabilities or not allowing technical assessment, prepare an exit strategy.
Strengthen Your Vendor Ecosystem with IBN Technologies
The security of your organization depends on how secure the weakest point in your supply chain is. Going above just a questionnaire for VAPT, actively validating the vendor VAPT ensures that your vendors don’t become easy entry points for attacks.
A third-party audit process and remediation enforcement requires certified skills. IBN Technologies assists companies in proactively managing cyber risks from third parties via VAPT and Penetration Testing (VAPT) services.
Key Reasons to Partner with IBN Technologies:
- Complete VAPT Expertise: Complete testing of vendor applications, API’s, Networks, Cloud environments and third-party integrations.
- Hybrid Testing Approach: Combination of automated vulnerabilities scanning and manual penetration testing to catch realistic security problems with zero false positives.
- Actionable Reporting: Detailed report, CVSS based risk prioritization and remediation advice for immediate action on vulnerabilities.
- Compliance Alignment: Compliance-driven assessments for international and local regulations such as ISO 27001, SOC 2, PCI DSS, HIPPA, GDPR, CERT-In, RBI, SEBI and DPDP.
- Remediation & Retesting: End-to-end support and on-demand re-testing to verify that identified vulnerabilities are completely patched before granting network access.
- Continuous Monitoring Options: Continuous awareness of vendor risk through periodic evaluations and integration with Managed SOC services.
Gain the confidence that your vendor ecosystem is secure, compliant, and resilient against emerging cyber threats.
Contact IBN Technologies today to schedule a third-party security assessment with our certified cybersecurity specialists.
Need VAPT Services for your 2026 project?
Get a free consultation with our tech team — no commitment.
Frequently Asked Questions
A Vulnerability Assessment involves using automated scanners to detect and list potential security vulnerabilities in vendor systems. A Penetration Test involves manually testing and, where authorized, exploiting identified vulnerabilities to understand how a breach could affect vendor operations and data.
Immediate action may include implementing compensating controls, such as isolating the vendor’s connection in a separate DMZ or sandbox environment, limiting permissions, and enforcing Multi-Factor Authentication (MFA). Organizations should also establish an SLA-based timeline for remediation and retesting.
IBN Technologies provides hybrid VAPT assessments that combine automated scanning with manual penetration testing to identify and validate security vulnerabilities. The service includes compliance-focused reports aligned with frameworks such as ISO 27001, SOC 2, PCI DSS, CERT-In, and DPDP, along with on-demand retesting to verify remediation.