Choose SOC 2 first if your immediate sales pipeline is dominated by US-based SaaS and technology buyers asking for a SOC 2 report.
Choose ISO 27001 first if international customers, procurement teams or regulated organisations want a recognised information-security certification.
Choose both if different strategic customers request different forms of assurance. Build one shared control and evidence programme, then sequence the audits instead of treating them as two unrelated projects.
We provide end-to-end support for SOC 2 and ISO 27001, from assessment and implementation to audit readiness.
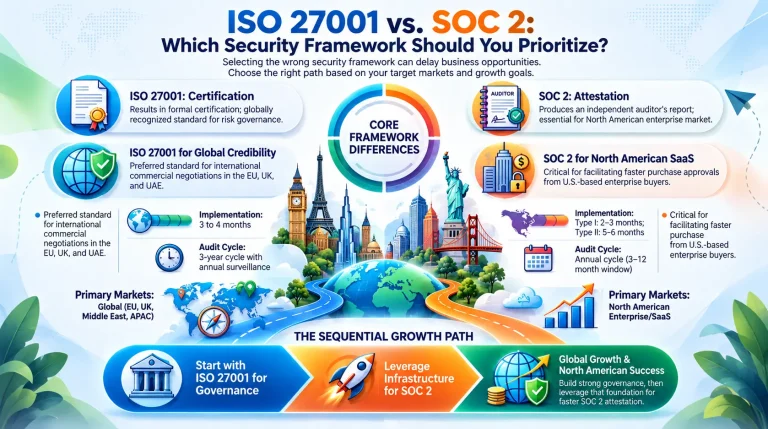
The key difference is the deliverable: ISO 27001 leads to certification of a defined Information Security Management System, while SOC 2 produces an independent attestation report on controls supporting a defined service.
Why ISO 27001 or SOC 2 decision matters
The right security framework can support both compliance and business growth. It can influence procurement decisions, simplify responses to security questionnaires, define required controls and records, and establish consistent security practices. Selecting a framework that fails to align with your buyers expectations can create unnecessary work and potentially delay important business opportunities.
When ISO 27001 Makes More Sense for Indian Businesses
ISO 27001 would be especially beneficial for Indian businesses operating with international clientele. Since it has been acknowledged internationally, it tends to carry more weight during international commercial negotiations. As an illustration, a company that offers cybersecurity services in Pune dealing with its clients based in Germany, the UK, and the UAE will find ISO 27001 useful in building its credibility early in the sales process. The potential clients in the regions are most likely familiar with this standard and would consider it to be the sign of systematic risk management.
When SOC 2 Should Be Your First Priority
SOC 2 is usually a more desirable choice when it comes to Indian companies catering to customers in the United States. As many American companies need SOC 2 in their vendor assessment, getting it can facilitate faster purchase approval process and help create confidence among potential customers.
As an instance, an Indian software-as-a-service firm operating out of Bengaluru that deals with providing workflow automation software to U.S. companies will benefit more from SOC 2 than ISO 27001 certification soon. This is because U.S. enterprise buyers typically mandate a SOC 2 Type II report during vendor risk assessments.
ISO 27001 vs SOC 2: What Is the Actual Difference?
| Feature
|
ISO/IEC 27001 | SOC 2 |
| Deliverable | Formal ISO 27001 Certification | Independent CPA Attestation Report (Type I or Type II) |
| Primary Focus | Information Security Management System (ISMS) & Risk Governance | Control Design (Type I) & Operating Effectiveness (Type II) |
| Audit Cycle / Term | 3-year certification cycle with annual surveillance audits | Annual audit cycle covering a rolling 3–12-month observation window |
| Implementation Timeline | 3 to 4 months | Type I: 2–3 months
Type II: 5 – 6 months max is needed (min 3 months observation period)
|
| Primary Markets | Global markets (EU, UK, Middle East, APAC) | North American enterprise and SaaS buyers |
| Core Business Value | Establishes long-term security governance and international trust | Accelerates enterprise vendor risk assessment (VRA) cycles in North America |
Which Framework Do Growing Indian SaaS Companies Usually Choose?
Most of the fast-growing Indian SaaS companies follow a sequential process for their compliance needs. Many of them start their journey by getting the ISO 27001 certification, which lays a solid base of security governance, risk management, policies, and processes for the company. With the help of these controls, the companies leverage the same security infrastructure to earn a SOC 2 Type II attestation report.
This way, these organizations ensure that all their efforts are optimized towards achieving the compliance requirements of the American market as well.
Conclusion
The choice between ISO 27001 and SOC 2 depends on your customers and growth goals. If you provide your services to international markets, ISO 27001 will have wider recognition internationally. In case you focus on enterprise clients from the USA, SOC 2 compliance will help you to fulfil vendor assurance needs and speed up sales process. For businesses targeting both markets, a unified compliance program covering both frameworks yields the highest ROI.
IBN Technologies simplifies ISO 27001 and SOC 2 compliance through an end-to-end process covering gap assessments, risk management, policy formulation, audit preparation, and continuous monitoring.
Ready to get started? Connect with IBN Technologies to simplify your compliance journey and build customer trust with confidence.
Need SOC 2 Services for your 2026 project?
Get a free consultation with our tech team — no commitment.
Frequently Asked Questions
ISO 27001 is an international standard for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS). SOC 2 is an independent attestation report issued by a CPA firm that evaluates controls against the Trust Services Criteria. Type I evaluates the design of controls at a point in time, while Type II evaluates their operating effectiveness over a period of time.
Absolutely. Since there is considerable commonality in security controls, policies, procedures, and evidence, organizations can develop a unified compliance plan and coordinate the audits in an appropriate order to improve efficiency.
The timeline varies depending on the organization's scope, existing controls, readiness, and remediation requirements. ISO 27001 certification may take several months, while SOC 2 Type I typically requires less time than Type II. A Type II examination also requires a defined observation period, commonly several months, to evaluate the operating effectiveness of controls.